AWS NAT Gateway Billing: Why You Are Paying for Ghost Infrastructure
Quick summary: An idle NAT Gateway in us-east-1 costs $36.50/month before any traffic: $32.85 in hours plus $3.65 for the public IPv4. A Regional NAT Gateway across three AZs still bills three hours, $109.50 idle.
Key Takeaways
- An idle NAT Gateway in us-east-1 costs $36.50/month before any traffic: $32.85 in hours plus $3.65 for the public IPv4
- A Regional NAT Gateway across three AZs still bills three hours, $109.50 idle
- As of 9 October 2026, the AWS price list charges a NAT Gateway in us-east-1 $0.045 per hour and $0.045 per GB processed
- Add the public IPv4 at $0.005 per hour and an idle gateway is $36.50 per month before a single packet
- Three Availability Zones, whether you deploy three zonal gateways or one Regional NAT Gateway active in all three, are $109.50 idle
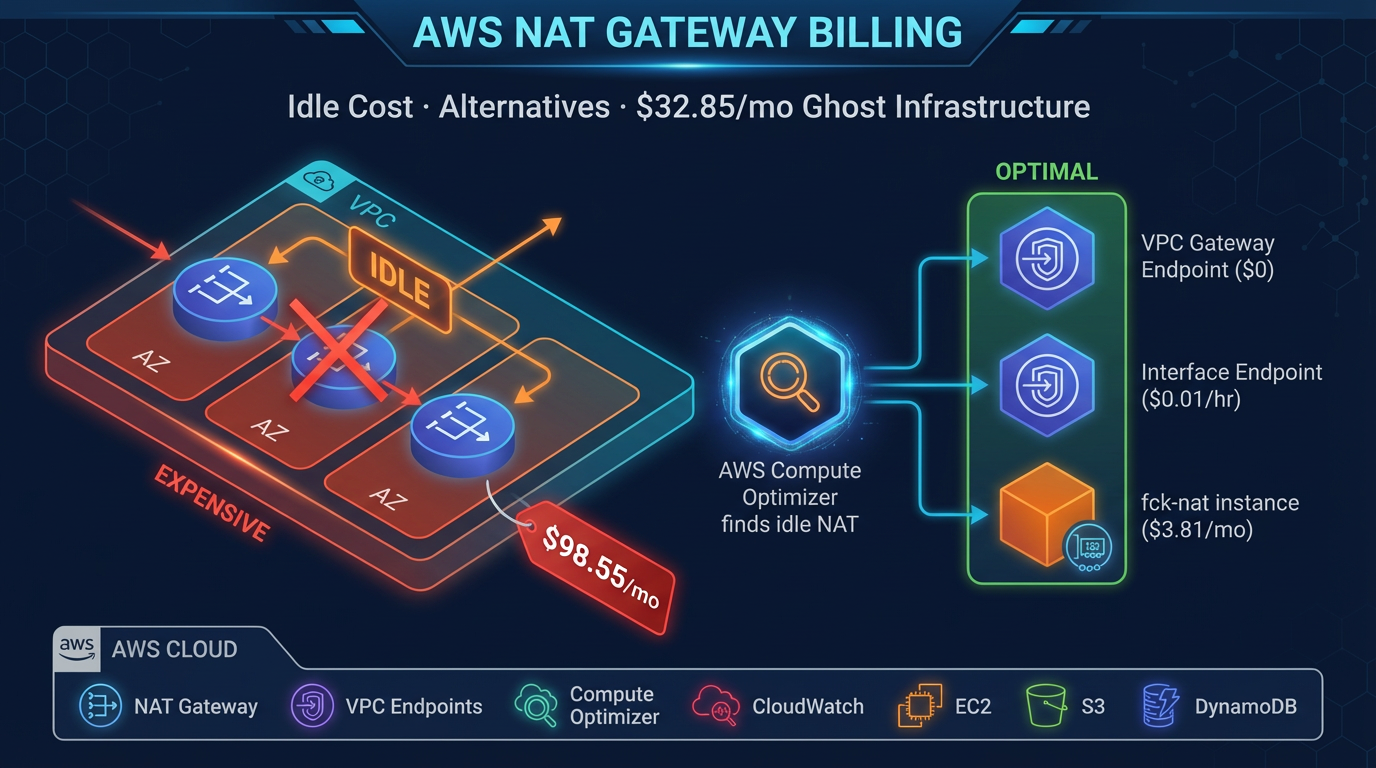
Table of Contents
As of 9 October 2026, the AWS price list charges a NAT Gateway in us-east-1 $0.045 per hour and $0.045 per GB processed. Add the public IPv4 at $0.005 per hour and an idle gateway is $36.50 per month before a single packet. Three Availability Zones, whether you deploy three zonal gateways or one Regional NAT Gateway active in all three, are $109.50 idle.
A startup architect still deploys that three-AZ layout for high availability, then leaves it processing nothing. Compute Optimizer can find the unused ones. The bill math below is what to run before you add the next gateway. Price this VPC in the NAT Gateway calculator. Size a NAT instance with the EC2 pricing calculator before you swap the managed gateway for one.
The detection tooling is real and newer than the rate card. In November 2025, AWS Compute Optimizer launched unused NAT Gateway recommendations. In February 2026, Trusted Advisor picked up the same signals. June 2026: the free 32-day lookback catches gateways that only spike during a month-end batch. When Cost Explorer surfaces the line, Analyze with Amazon Q narrates the drivers (Cost Explorer guide).
The five-line NAT bill
AWS bills five charges. Hours and the public IPv4 accrue while the gateway exists. The other three follow the bytes. Figures below use a 730-hour month (8,760 hours a year ÷ 12). Each partial NAT Gateway-hour is billed as a full hour. Rates: Amazon VPC pricing.
Gateway hours. $0.045 per hour in us-east-1. One gateway is $0.045 × 730 = $32.85.
Public IPv4. $0.005 per hour for the address on the gateway, the same rate in every commercial region since February 2024. One address is $0.005 × 730 = $3.65.
Data processing. $0.045 per GB in us-east-1 for every gigabyte that passes through the gateway, in either direction. Return traffic from the internet is processed. General data transfer into AWS has no charge of its own. The NAT processing fee still applies to those bytes.
Cross-AZ transfer. $0.01 per GB in each direction when the workload and the gateway sit in different Availability Zones. That is $0.02 per GB of one-way payload. A NAT Gateway in the same AZ as the workload avoids this line.
Data transfer out. $0.09 per GB for the first 10 TB that leaves the VPC for the internet in us-east-1, on top of processing. AWS includes 100 GB per month of data transfer out to the internet, aggregated across services and regions except China and GovCloud. The tables below show the gross egress charge. That allowance can cover a small NAT egress line only when the rest of the account has not already used it.
At 10 GB processed and no cross-AZ traffic, fixed charges are about 99% of the NAT bill: $36.50 of the $36.95 total. The 10 GB of processing adds $0.45. Under about 50 GB a month, deleting an unused gateway beats tuning the per-GB rate.
us-east-1, hours + public IPv4 + processing. Egress is the extra column if that entire GB volume is outbound. Processing counts both directions, so a real bill’s outbound GB is smaller than processed GB.
| Monthly GB processed | 1 AZ | 2 AZs | Gross egress if all of that GB leaves AWS |
|---|---|---|---|
| 0 | $36.50 | $73.00 | $0 |
| 10 | $36.95 | $73.45 | $0.90 |
| 500 | $59.00 | $95.50 | $45.00 |
| 1,000 | $81.50 | $118.50 | $90.00 |
Worked 500 GB, one AZ, no cross-AZ: $32.85 hours + $3.65 IPv4 + (500 × $0.045) processing = $59.00. Two AZs double the hours and the addresses, not the processing, when the GB figure is the total through both gateways.
Three idle AZs are $109.50. That is three times $36.50, zonal or Regional.
Hourly and per-GB rates from the AWS price list published 9 October 2026. Public IPv4 is $0.005 per hour in each region. Idle month = (hourly × 730) + $3.65.
| Region | Per hour and per GB | Idle, 1 AZ |
|---|---|---|
| us-east-1 (N. Virginia) | $0.045 | $36.50 |
| eu-west-1 (Ireland) | $0.048 | $38.69 |
| eu-west-2 (London) | $0.050 | $40.15 |
| eu-central-1 (Frankfurt) | $0.052 | $41.61 |
When the gateway exists for a partner allowlist
Lambda outside your VPC does not keep a stable outbound address, so a partner API that allowlists one IP pushes the function into a VPC with a NAT Gateway. At 10 GB a month that gateway still costs $36.50 in us-east-1 before processing. The address is the product. The hour is the tax.
For that low-volume HTTPS allowlist, a NAT instance or fck-nat on a t4g.nano is about $4 in instance hours, plus the same $3.65 public IPv4, plus the same internet egress, and no per-GB NAT processing fee. You patch the instance. There is no NAT Gateway SLA. Failover is a route-table update, often 30–60 seconds. Dev and test, and production teams who accept that window, are the fit. A whole VPC that moves hundreds of gigabytes to the internet still belongs on the managed gateway.
Reproduce this — NAT Gateway pricing calculator. Set the region, the gateway count (one per active AZ), processed GB, one-way cross-AZ GB, and outbound GB. Idle us-east-1, one gateway, zeros everywhere, is $36.50. Ten GB processed, no cross-AZ, no egress, is $36.95.
Why Idle NAT Gateways Accumulate
Idle NAT Gateways are not accidents—they are the result of predictable patterns in how infrastructure evolves:
Dev and test environments never cleaned up. A developer spins up a VPC with a NAT Gateway to test an application. The project gets shelved. The VPC is abandoned. The NAT Gateway remains, billing the account at $36.50/month in us-east-1 until someone audits the infrastructure.
Disaster recovery standby gateways. A 3-AZ production setup deploys with route tables pre-configured to fail over to a secondary NAT Gateway in a different AZ. That secondary gateway sits idle almost all the time, yet it costs $36.50/month to exist.
Orphaned VPC peering. An application originally required cross-region communication through a NAT Gateway for compliance reasons. The requirement changed, the traffic stopped, but the gateway was never deleted.
“Just in case” infrastructure. Architects deploying to a new region provision a full 3-AZ NAT Gateway setup with the standard architecture, then discover the application never needed it.
Each of these follows from reasonable decision-making at the time. The problem is that idle NAT Gateways generate no alarms, no alerts, and no visible cost signals. They silently bill each month, month after month, year after year.
AWS Compute Optimizer: Finding Idle NAT Gateways
In November 2025, AWS added the capability many wished for years earlier: automated detection of unused NAT Gateways.
How it works: AWS Compute Optimizer analyzes 32 days of CloudWatch metrics for each NAT Gateway. It flags a gateway as unused if it meets all three conditions:
- Zero active connections over the 32-day period
- Zero incoming packets from source (your resources)
- Zero incoming packets from destination (remote systems)
The 32-day window is long enough to capture normal traffic patterns; gateways used only occasionally will not be flagged.
Smart enough to avoid false positives: Compute Optimizer checks route table associations. If a gateway is associated with a route table but not actively handling traffic, it avoids flagging failover-only standby gateways—those pre-configured to take traffic only during disaster recovery when an application swaps route tables dynamically.
How to use it:
- Open AWS Compute Optimizer in the AWS Console
- Navigate to NAT Gateways and opt in to recommendations
- Within 24 hours, recommendations appear with detailed cost savings estimates
- Cross-reference with AWS Cost Optimization Hub for a centralized view alongside other cost-reduction actions
- In February 2026, AWS enhanced Trusted Advisor with the same signals; activate Trusted Advisor checks to surface unused gateway recommendations
The catch: Compute Optimizer gives you detection and a recommendation to delete. It does not tell you whether deleting that gateway will break a failover process, a legacy application, or an undocumented dependency. Always verify before deleting.
Tier 1: Free Alternatives — VPC Endpoints
The best alternative is often free.
VPC Gateway Endpoints for S3 and DynamoDB eliminate the need for NAT Gateway for those specific services entirely. Instead of routing traffic through a NAT Gateway to the public AWS API, you configure a gateway endpoint, and traffic stays within the VPC and AWS network. Cost: $0.00.
This is the first optimization to make. If your application talks to S3 or DynamoDB from private subnets, configuring a gateway endpoint removes that traffic from the NAT Gateway entirely and eliminates NAT Gateway charges for that portion of your data transfer.
VPC Interface Endpoints (PrivateLink) extend the concept to nearly every AWS service: ECR, CloudWatch, Secrets Manager, SSM, SQS, SNS, and hundreds more. Instead of routing through NAT Gateway to a public API endpoint, traffic stays private within the VPC.
Cost: $0.01/hour per endpoint + $0.01/GB of data processed. For most services, this is significantly cheaper than NAT Gateway ($0.045/hr + $0.045/GB).
Real-world example: A team using Datadog logs from private subnets. All log traffic went through NAT Gateway at $0.045/GB processing + $0.09/GB egress = $0.135/GB. Switching to a Datadog VPC Interface Endpoint costs $0.01/GB. For 500GB/month: NAT Gateway cost $67.50, VPC endpoint cost $5.00. Savings: $62.50/month, $750/year, with zero application code changes.
Egress-Only Internet Gateway serves IPv6 traffic without requiring a NAT Gateway. Cost: $0.00, AWS-managed with 99.99% SLA. This is the future-forward option for applications moving to IPv6.
Tier 2: 90% Savings — fck-nat and NAT Instances
For workloads requiring general internet access (not just AWS service calls), fck-nat is the production-ready alternative that saves 90% on NAT infrastructure costs.
fck-nat is a modern, actively maintained open-source project that runs a NAT instance on a t4g.nano or t4g.micro EC2 instance. It handles IP masquerading and connection tracking, delivering NAT functionality without paying AWS’s managed NAT Gateway premium.
Cost breakdown:
- t4g.nano base cost: ~$3.00/month
- No per-GB data processing fee (unlike NAT Gateway at $0.045/GB)
- Data egress still charged at $0.09/GB (same as any EC2-based egress)
- Total for light traffic: about $4/month in instance hours, plus the same $3.65 public IPv4, versus $36.50 idle for a managed gateway in us-east-1
Trade-offs:
- No AWS SLA (managed NAT Gateway has 99.99% availability)
- Failover is manual—if the EC2 instance fails, you must update route tables to point to a secondary NAT instance (can take 30–60 seconds vs. AWS’s automatic failover)
- You own the EC2 instance: patching, monitoring, troubleshooting
Best for: Dev/test environments, cost-sensitive production teams comfortable managing the EC2 instance, startups where the operational trade-off is worth the 90% savings.
The DIY NAT Instance: If fck-nat feels like adding a new dependency, the DIY approach is simpler than it sounds. Launch a t4g.nano EC2 instance with Amazon Linux, disable source/destination checking, and run iptables -t nat -A POSTROUTING -j MASQUERADE to enable IP masquerading. Cost is identical (~$3.81/month base), but you manage the configuration yourself.
Terraform modules are available for both fck-nat and DIY NAT instances if you want infrastructure-as-code setup.
Tier 3: Regional NAT Gateway
AWS offers a Regional NAT Gateway that expands and contracts with the Availability Zones your workloads use, and it simplifies route tables. The hourly charge stays one NAT Gateway-hour per Availability Zone the gateway is active in.
From the VPC pricing page: you are charged for each hour the NAT Gateway is configured in each Availability Zone. A regional gateway running in three AZs for one hour is three NAT Gateway-hours. In us-east-1 that is $0.045 × 3 = $0.135 per hour, $98.55 per month in hours, plus $3.65 per public IPv4. With one address per active AZ the idle total is $109.50, the same base as three zonal gateways. When the gateway drops an AZ, billing for that AZ stops.
Data processing and internet egress stay per GB. Cross-AZ transfer still applies when a workload and the gateway’s path are in different AZs.
Use it when you want the managed SLA and automatic AZ coverage, and you have priced one hour per AZ you will actually run. Keep fck-nat or a NAT instance when the traffic is a low-volume allowlist and you will own patching and failover.
Optimization Without Changing Gateway Type
If you keep NAT Gateways, minimize their cost with these patterns:
Same-AZ traffic routing: Route each subnet through a NAT Gateway in the same Availability Zone. Cross-AZ transfer is $0.01 per GB in each direction, so $0.02 per GB of one-way payload. One terabyte of one-way traffic from the other AZ is $20 per month. Same-AZ routing removes that line.
Audit traffic with VPC Flow Logs and CloudWatch Logs Insights. Identify which traffic actually needs NAT Gateway vs. which is calling AWS services that could use free VPC endpoints. Often 50%+ of NAT Gateway traffic can be redirected to VPC endpoints with zero code changes.
Transit Gateway centralization: For organizations with multiple VPCs, consolidating NAT Gateways via Transit Gateway reduces duplication and improves visibility.
Decision Framework: Which Alternative to Use
| Use Case | Approach | Cost | Trade-offs |
|---|---|---|---|
| S3/DynamoDB from private subnet | VPC Gateway Endpoint | Free | None—use this first |
| AWS service APIs (ECR, CloudWatch, SSM, etc.) | VPC Interface Endpoint | $7–15 | One endpoint per service |
| General internet, dev/test environment | fck-nat or NAT instance | ~$4 | No AWS SLA, manual failover |
| General internet, production, cost-sensitive | fck-nat with hot standby | ~$8 | Failover: 30–60 sec window |
| General internet, production, SLA required | NAT Gateway, one per active AZ | $36.50 per AZ idle in us-east-1 | Regional NAT bills the same per active AZ |
| General internet, several regions | NAT per region you serve | $36.50–$41.61 per AZ idle | Frankfurt is the high end of this set |
Related Resources
- AWS Data Transfer Costs: The Line Item That Breaks Startups — Deep dive into NAT Gateway’s role in the data transfer bill
- AWS Cost Optimization Hub Guide — How to centrally track cost-reduction recommendations
- AWS VPC Networking Best Practices for Production — Design patterns to minimize network cost
Start Here
If you have NAT Gateways, your action list is:
- Opt into AWS Compute Optimizer if you have not already (free)
- Review unused NAT Gateway recommendations — Compute Optimizer will find the obvious candidates
- Audit traffic with VPC Flow Logs — Identify which traffic could be redirected to VPC endpoints
- Implement VPC Gateway Endpoints for S3 and DynamoDB first — instant savings, zero code changes
- Implement VPC Interface Endpoints for other AWS services your application uses
- Re-count the gateways. One hour per active AZ, including a Regional NAT Gateway. If the only job is a partner allowlist at a few gigabytes, price fck-nat or a NAT instance against the $36.50 idle line.
Gateway Endpoints for S3 and DynamoDB remove that traffic at no charge. A NAT instance removes the NAT hourly and per-GB processing charges and leaves you with the instance, the public IPv4, and internet egress.
Price this VPC, then book a cost audit if the NAT line is still one of the top rows in Cost Explorer.
Frequently asked questions
How much does an idle NAT Gateway cost per month?
Does a Regional NAT Gateway cost less than one gateway per Availability Zone?
Does a NAT Gateway charge for traffic coming back from the internet?
What is the cheapest alternative to AWS NAT Gateway?
How does AWS Compute Optimizer find idle NAT Gateways?
Is fck-nat safe to use in production?
Should I replace NAT Gateway with a NAT instance?
AWS Cloud Architect & AI Expert
AWS-certified cloud architect and AI expert with deep expertise in cloud migrations, cost optimization, and generative AI on AWS.